
Do you know where your AI agents are? We'll show you.
Get a hands-on risk assessment of your own environment. We inventory the agents, service accounts and API keys across your connected systems, watch MCP tool calls in monitor-only mode, and walk you through what we find.
Monitor-only. Nothing is blocked. No cost.
Trusted by the world's most innovative companies




Your IAM program stops at login. Agents act after it.
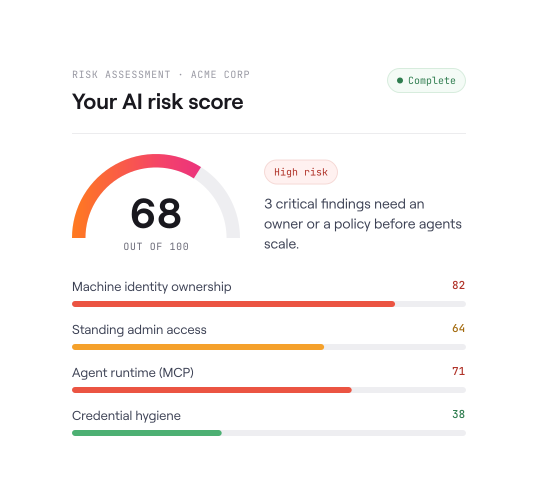
Machine identities already outnumber your people, and your board is asking about AI risk. Recent threat research showed attackers using AI agents to reach privileged cloud access in under three hours. You can't govern what you can't see.

of non-human identities have no assigned owner.
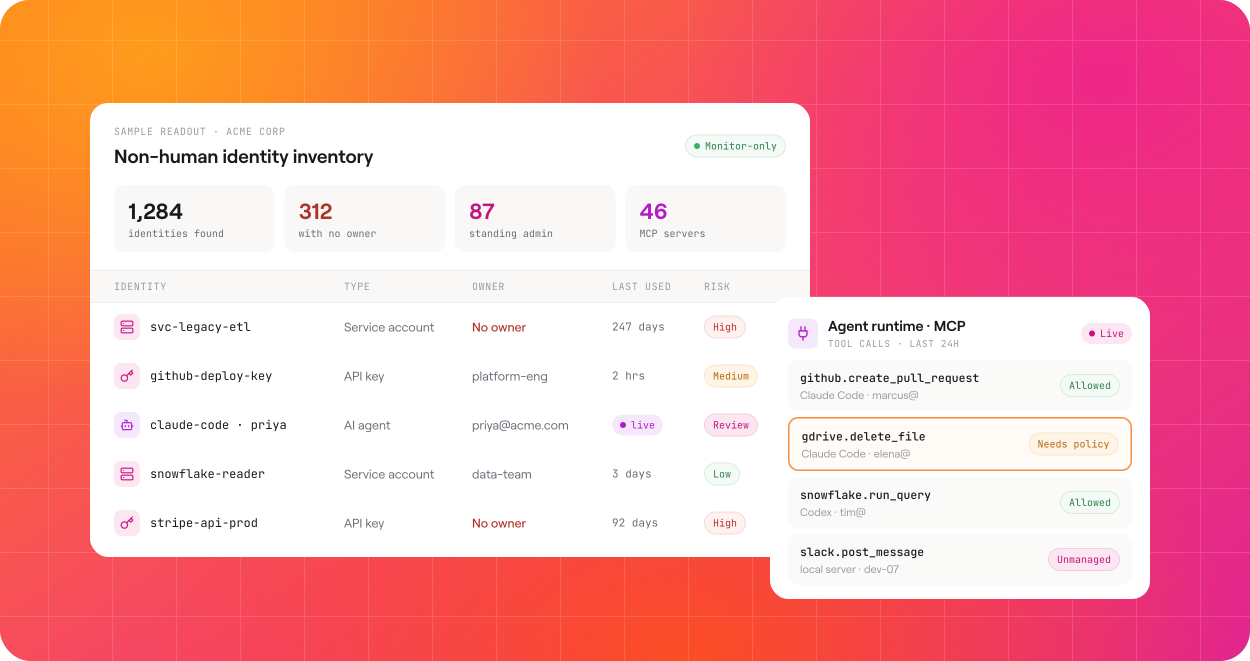
What's in your AI agent and NHI risk assessment
We look at the two places agent risk lives: the identities agents run on, and what agents do with them.
01: Non-human identities
Inventory of agents, service accounts and API keys across your connected systems
Credentials with no owner, no recent activity, or more access than they use
Where machine identities hold standing admin or privileged access
02: Agent runtime (MCP)
Every MCP server and tool in use in Claude Code, Codex, and more, including ones developers added locally
Which tools agents call, how often, and tied back to the person running the agent
Calls you would want an allow or deny policy for
What you get from the readout
Your NHI inventory
A map of agent and MCP activity
Your top risks, ranked
A recommended policy set
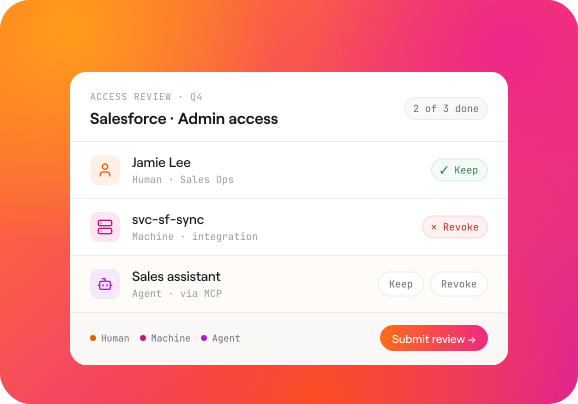

One platform for human, machine and agent access
Lumos extends the governance your team already runs (access reviews, just-in-time access, offboarding) to AI agents. MCP servers and agent tools can be brought into the same access reviews and policies, in the same audit trail.
Frequently Asked Questions

An NHI risk assessment finds the service accounts, API keys and tokens across your connected systems, and flags the ones with no owner, no recent use, or too much access. Lumos adds a review of how AI agents use those credentials at runtime.
Yes. Lumos integrates read-only with the real systems in your environment, so findings reflect what is actually connected and running, not answers to a questionnaire.
The assessment runs about [X weeks]: a 30-minute scoping call, setup, [X days] of monitor-only observation, then a readout with your team.
No. In monitor-only mode, policies default to allow, so agents and developers keep working. You choose if and when to turn on enforcement.
Lumos MCP Governance supports Claude Code, Codex, Cursor, Antigravity CLI and Claude Cowork, with Microsoft Copilot coming soon. It works on macOS, Windows and Linux, though coverage varies by agent. Lumos installs a hook that checks each tool call before it runs, so there is no gateway or traffic rerouting.
No. Lumos stores tool call metadata and, optionally, call arguments. It does not store prompts, responses or results.
Policy checks target under 50 milliseconds per tool call.
Lumos can delete the data collected during the assessment once it's complete.
Yes. There is no cost and no commitment.


Find your agents before an attacker does.
Get a clear picture of your AI agents and the identities they run on, from your own environment, in 3 weeks.
Request your free assessment
The autonomous identity platform. Agents that continuously govern access for every human, machine, and AI.