
Do you know where your AI agents are? We'll show you.
Get a hands-on risk assessment of your own environment. We inventory the agents, service accounts and API keys across your connected systems, watch MCP tool calls in monitor-only mode, and walk you through what we find.
Top findings

Service accounts with no owner
API keys with standing admin access
MCP servers developers added locally
Agent tool calls that need a policy
Trusted by the world's most innovative companies




Your IAM program stops at login. Agents act after it.
Machine identities already outnumber your people, and your board is asking about AI risk. Recent threat research showed attackers using AI agents to reach privileged cloud access in under three hours. You can't govern what you can't see.

of non-human identities have no assigned owner.
What's in your AI agent and NHI risk assessment
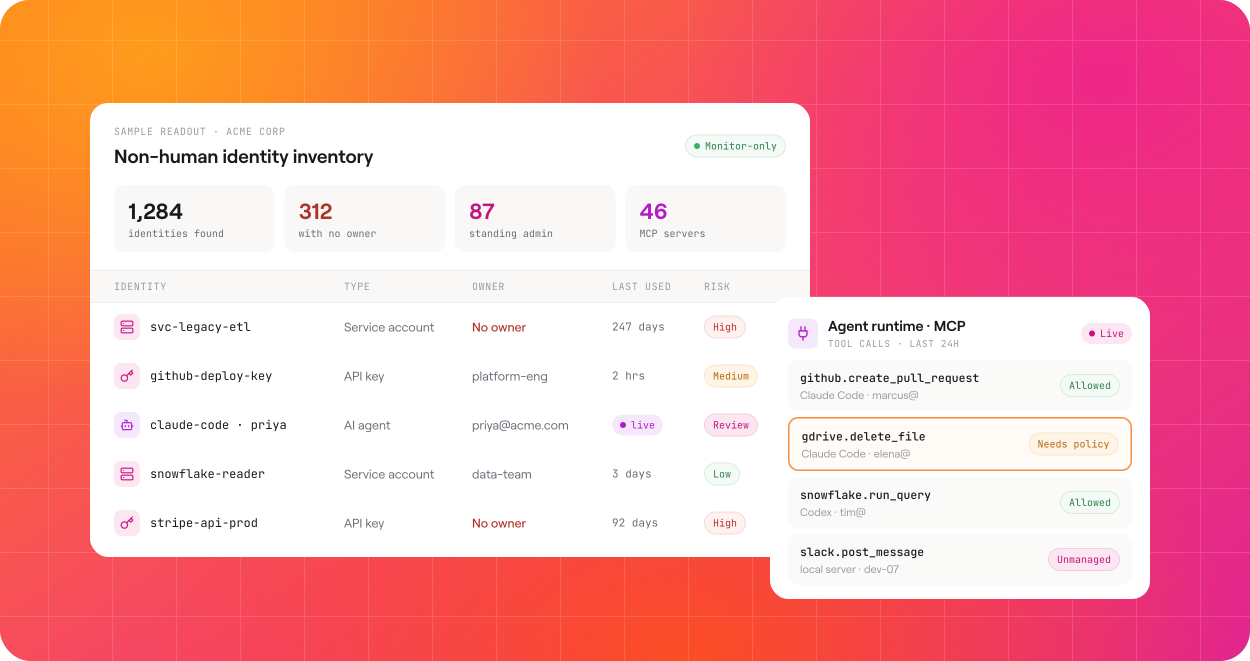
We look at the two places agent risk lives: the identities agents run on, and what agents do with them.
01: Non-human identities
Inventory of agents, service accounts and API keys across your connected systems
Credentials with no owner, no recent activity, or more access than they use
Where machine identities hold standing admin or privileged access
02: Agent runtime (MCP)
Every MCP server and tool in use in Claude Code, Codex, and more, including ones developers added locally
Which tools agents call, how often, and tied back to the person running the agent
Calls you would want an allow or deny policy for
What you get from the readout
Your NHI inventory
A map of agent and MCP activity
Your top risks, ranked
A recommended policy set
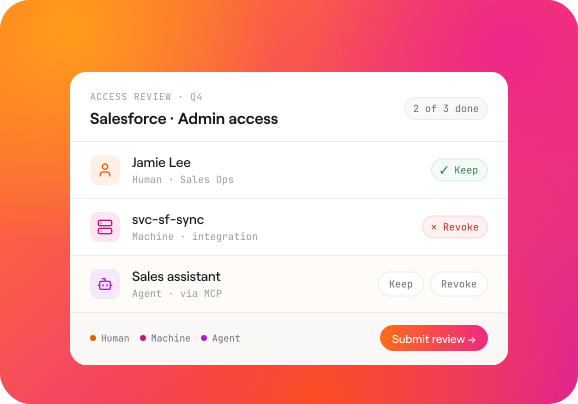

One platform for human, machine and agent access
Lumos extends the governance your team already runs (access reviews, just-in-time access, offboarding) to AI agents. MCP servers and agent tools can be brought into the same access reviews and policies, in the same audit trail.
{{ Frequently Asked Questions - UPDATE THESE }}

Identity Security Posture prioritizes who has what and how it’s used—finding misconfigurations, SoD conflicts, and excess privilege—then triggers governed fixes. It complements IGA (enforcement/workflows) and SIEM (event detection).
Albus correlates HRIS, IdP, app, and usage signals; builds peer baselines; and flags outliers (toxic combos, dormant/orphaned access, privilege spikes). Every finding includes rationale so teams know why it’s risky and what to fix first.
That's up to you! Use preventive guardrails (JIT, time-bound, inactivity revocation) and/or require owner approval. Closed-loop workflows enforce removals, capture evidence, and sync back to ITSM and Lumos platform.
Yes. Service accounts, keys, workload/agent identities, and shadow IT/AI are discovered and monitored with entitlement-level context, so you can reduce blast radius across humans and machines.
Yes. Service accounts, keys, workload/agent identities, and shadow IT/AI are discovered and monitored with entitlement-level context, so you can reduce blast radius across humans and machines.


Find your agents before an attacker does.
Get a clear picture of your AI agents and the identities they run on, from your own environment, in 3 weeks.
Request your free assessment
The autonomous identity platform. Agents that continuously govern access for every human, machine, and AI.